Key Takeaways
- Providers in this market can look identical on their websites and differ significantly in what they actually do.
- The four categories—MSP with security, MSSP, consultancy, and product vendor—solve different problems.
- Response authority is one of the most revealing questions to ask. Detection without the ability to act is monitoring.
- Ask what the monthly evidence looks like, because that is what an auditor and an insurer will want.
What are the four categories, and which do you need?
A cybersecurity service provider delivers security capability as an ongoing service rather than as software you operate yourself. The market divides into four broad categories: managed IT providers with security included, dedicated managed security service providers, consultancies that advise without operating, and product vendors selling tooling.
A cyber security services company may describe itself in broad terms, but the category underneath that language matters. These four models solve different problems.
| Category | What they do | Best when |
|---|---|---|
| MSP with security included | Run IT operations with security as part of the service | You need both and want one accountable party |
| Dedicated MSSP | Operate security functions only, alongside your IT | IT is handled and security specifically is not |
| Consultancy | Assess, advise, design. They do not operate | You need a strategy, assessment, or audit response |
| Product vendor | Sell tooling you or someone else operates | You have the team to run it |
The error we see most often is buying a product when the gap was operational. More tooling into an unwatched queue does not improve detection; it increases noise.

Which questions actually separate providers?
Marketing claims converge. Operational answers do not. These six questions reveal how the provider actually operates.
When evaluating a cybersecurity service provider, ask questions that expose what happens after an alert rather than simply what technology the provider uses.
| Icon | Question | What the answer reveals |
|---|---|---|
| Clock | What are your coverage hours, literally? | Whether 24/7 means staffed operations or an answering service |
| Zap | What can you do without contacting us? | Whether you are buying a service or a notification feed |
| Filter | Who triages, and what share never reaches us? | Whether you will drown in false positives |
| File | What is in the monthly report? | Whether the evidence survives an audit |
| Tool | How is detection tuned to our environment? | Whether they understand that baselines take weeks |
| Log out | What happens if we leave? | Whether documentation and data come with you |
When comparing cybersecurity vendors, these questions reveal more about the service than a list of technologies.
Response authority is the highest-yield of the six. If the provider must call you before isolating a compromised device at 3am, the 3am decision is still yours.
CISA’s guidance for organizations working with managed providers is explicit that the division of responsibility should be documented and understood by both sides rather than assumed.
What should be in the monthly evidence?
Reporting is where the difference between a service and a subscription becomes visible, and it is the part buyers often examine least during selection.
A useful monthly report should show:
- What was detected, and what was closed without reaching you
- What actions were taken, by whom, and under what authority
- Patch and vulnerability state across the estate, not just a count
- Open infrastructure gaps, named, with a status
- Changes to access and privileged accounts
- What remains outstanding from last month
The last item is the tell. A report that only lists closed work is a marketing document. A report that carries forward what is still open is an operational record.
The NIST Cybersecurity Framework splits the work into Identify, Protect, Detect, Respond, Recover and Govern. A useful test of any monthly report is how many of those six areas it gives you evidence for, because many security reports focus heavily on Detect while governance evidence may be less visible.
Ask to see a sample with client details removed before you sign. A provider who cannot produce one is telling you something useful.
How does this fit alongside an existing IT provider?
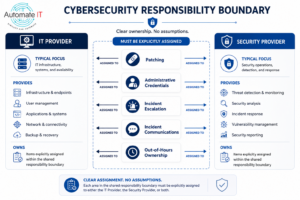
Many organizations end up with both an IT provider and a security provider, which works when the boundary is written down and fails when it is assumed.
- Agree which party owns patching, because both will assume the other does.
- Agree who holds administrative credentials and how they are shared or separated.
- Agree the escalation path when an incident crosses the boundary.
- Agree who talks to the client during an incident, so you are not managing two narratives.
- Put all four in writing before go-live rather than discovering them during an event.
Where one provider covers both, the boundary between providers is reduced, but you trade that for concentration risk. Neither answer is wrong; the mistake is not choosing deliberately.
Our Security as a Service operates alongside Managed IT Services and Managed IT 360 under a single accountability line, which reduces the boundary problem at the cost of consolidating suppliers.
What does good look like after six months?
A useful test at selection is to ask what the engagement should look like half a year in. Vague answers predict vague delivery.
By six months, you should expect to see evidence that:
- Alert volume reaching your team has fallen, not risen
- Detection is tuned, so what does arrive is usually real
- You can answer an auditor’s access and patch questions from existing reports
- Known-unpatchable equipment is documented with compensating controls
- There is a shorter list of open gaps than at month one, with dates against the remainder
If none of that has happened, it is worth questioning whether the service is materially changing your risk, which is the outcome you are actually buying.
For an independent baseline to measure against, CISA’s Cyber Essentials is a public reference no provider controls.
Client Case Card
Client environment: A large hospital.
Problem: High problem-management burden.
Solution: Failure types mapped and automated, with proactive and predictive alerting.
Result: Problem management time reduced by 80%, with 100% availability.
This evidences operational monitoring maturity, not a security detection rate. No detection statistics are claimed.
Frequently Asked Questions
What is the difference between a cybersecurity provider and an MSP?
An MSP keeps IT running and may include security to varying depths. A dedicated security provider operates security functions specifically. Many organizations use both, and the important thing is that the boundary between them is written down rather than assumed.
Should we choose one provider for IT and security, or two?
Both work. One provider reduces the boundary problem but concentrates supplier risk. Two providers give you specialisation and create a gap that must be actively managed. What causes problems is arriving at either arrangement without deciding it.
How do we know if a provider is any good before signing?
Ask for a sample monthly report with client details removed, ask what they are authorised to do without contacting you, and ask for a reference call with a client of similar size and sector. Then actually make the call.
Do we need a provider if we already have security tooling?
It depends whether anyone is watching it. Tooling produces alerts; a service produces outcomes. If your alerts arrive into a queue reviewed the next working day, the tooling is not delivering what you bought it for.
